Rate this post

MS-101 Training & Certification Get Latest Microsoft 365 Updated on Jul 27, 2024

Certification Training for MS-101 Exam Dumps Test Engine

QUESTION 196
You need to recommend a solution for the security administrator. The solution must meet the technical requirements.
What should you include in the recommendation?


QUESTION 197
You have a Microsoft 365 E5 tenant that contains the devices shown in the following table.

You plan to implement attack surface reduction (ASR) rules. Which devices will support the ASR rules?


QUESTION 198
You have a Microsoft 365 E5 tenant that contains the users shown in the following table.

You purchase the devices shown in the following table.

In Microsoft Endpoint Manager, you create an enrollment status page profile that has the following settings:
Show app and profile configuration progress: Yes
Allow users to collect logs about installation errors: Yes
Only show page to devices provisioned by out-of-box experience (OOBE): No Assignments: Group2 For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

QUESTION 199
You have an Azure Active Directory (Azure AD) tenant and a Microsoft 365 E5 subscription. The tenant contains the users shown in the following table.

You plan to implement Microsoft Defender Advanced Threat Protection (Microsoft Defender ATP).
You verify that role-based access control (RBAC) is turned on in Microsoft Defender ATP.
You need to identify which user can view security incidents from the Microsoft Defender Security Center.
Which user should you identify?


QUESTION 200
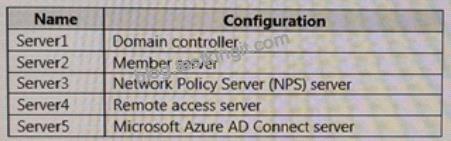
Your network contains an on-premises Active Directory domain that syncs to Azure Active Directory (Azure AD). The domain contains the servers shown in the following table.
You use Azure Information Protection.
You need to ensure that you can apply Azure Information Protection labels to the file stores on Server1.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.

QUESTION 201
You have retention policies in Microsoft 365 as shown in the following table.

Policy1 is configured as shown in the Policy1 exhibit. (Click the Policy1 tab.)

Policy2 is configured as shown in the Policy2 exhibit. (Click the

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

QUESTION 202
You have a Microsoft 365 E5 subscription linked to an Azure Active Directory (Azure AD) tenant. The tenant contains a group named Group1 and the users shown in the following table:

The tenant has a conditional access policy that has the following configurations:
Name: Policy1
Assignments:
– Users and groups: Group1
– Cloud aps or actions: All cloud apps
Access controls:
Grant, require multi-factor authentication
Enable policy: Report-only
You set Enabled Security defaults to Yes for the tenant.
For each of the following settings select Yes, if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

QUESTION 203
You have a Microsoft 365 E5 subscription that uses Microsoft Defender Advanced Threat Protection (Microsoft Defender ATP).
D18912E1457D5D1DDCBD40AB3BF70D5D
From Microsoft Defender ATP, you turn on the Allow or block file advanced feature.
You need to block users from downloading a file named File1.exe.
What should you use?


QUESTION 204
You have 2,500 Windows 10 devices and a Microsoft 365 E5 tenant that contains two users named User1 and User2. The devices are not enrollment in Microsoft Intune.
In Microsoft Endpoint Manager, the Device limit restrictions are configured as shown in the following exhibit.

In Azure Active Directory (Azure AD), the Device settings are configured as shown in the following exhibit.

From Microsoft Endpoint Manager, you add User2 as a device enrollment manager (DEM).
For each of the following statement, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

QUESTION 205
You have the Microsoft Azure Active Director (Azure AD) users shown in the following table.

You create a conditional access policy that has the following settings:
* The Assignments settings are configured as follows:
* Users and groups: Group1
* Cloud apps: Microsoft Office 365 Exchange Online
* Conditions: Include All device state, exclude Device marked as compliant
* Access controls is set to Block access.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

QUESTION 206
Your company has 10 offices.
The network contains an Active Directory domain named contoso.com. The domain contains 500 client computers. Each office is configured as a separate subnet.
You discover that one of the offices has the following:
Computers that have several preinstalled applications
Computers that use nonstandard computer names
Computers that have Windows 10 preinstalled
Computers that are in a workgroup
You must configure the computers to meet the following corporate requirements:
All the computers must be joined to the domain.
All the computers must have computer names that use a prefix of CONTOSO.
All the computers must only have approved corporate applications installed.
You need to recommend a solution to redeploy the computers. The solution must minimize the deployment time.
What should you recommend?


QUESTION 207
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft Azure Active Directory (Azure AD) tenant named contoso.com.
You create an Azure Advanced Threat Protection (ATP) workspace named Workspace1.
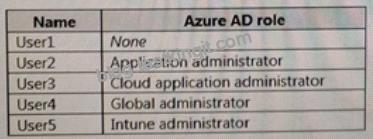
The tenant contains the users shown in the following table.
You need to modify the configuration of the Azure ATP sensors.
Solution: You instruct User4 to modify the Azure ATP sensor configuration.
Does this meet the goal?


QUESTION 208
You have a Microsoft 365 subscription.
All users have their email stored in Microsoft Exchange Online.
In the mailbox of a user named User1, you need to preserve a copy of all the email messages that contain the word Project X.
What should you do first?


QUESTION 209
Your company uses Windows Defender Advanced Threat Protection (ATP). Windows Defender ATP contains the device groups shown in the following table.

You onboard computers to Windows Defender ATP as shown in the following table.

Of which groups are Computer1 and Computer2 members? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

QUESTION 210
HOTSPOT
You have a Microsoft Azure Activity Directory (Azure AD) tenant contains the users shown in the following table.

Group3 is a member of Group1.
Your company uses Microsoft Defender Advanced Threat Protection (ATP). Microsoft Defender ATP contains the roles shown in the following table.

Microsoft Defender ATP contains the device groups shown in the following table.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Hot Area:


Step by Step Guide to Prepare for MS-101 Exam: https://www.testkingit.com/Microsoft/latest-MS-101-exam-dumps.html

Related Links: telegra.ph fortunetelleroracle.com myportal.utt.edu.tt myportal.utt.edu.tt www.stes.tyc.edu.tw fortunetelleroracle.com